QCIMBTQRequest evaluation ↗Contact
In development

QCIM Platform Security

Billions of devices will soon find themselves in operating environments outside what they were engineered for. QCIM Platform Security monitors the ecosystem and supplies cryptographic research, secure updates, device measurement, and policy management to hardware Root-of-Trust products so they can stay ahead of threats to their most sensitive hardware components.

QCIM security stack

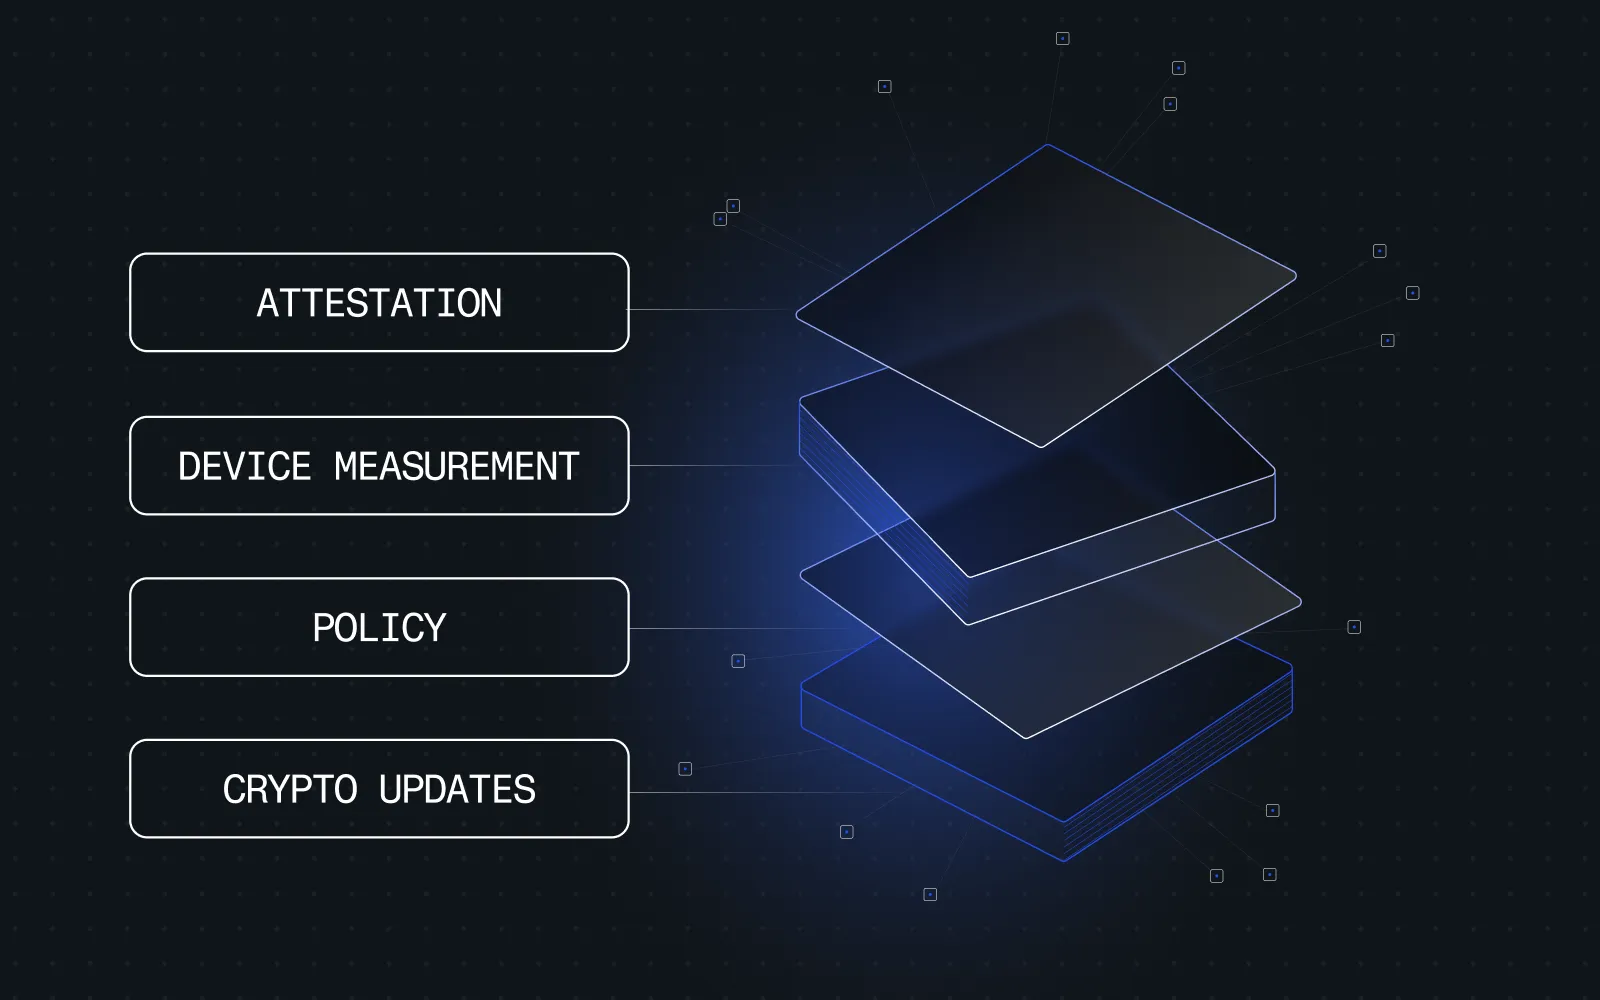
Where QCIM Platform Security sits in the stack.

The Engine executes the cryptography, the Root of Trust establishes device trust, and the Platform maintains that trust after deployment.

What the platform does

Platform capabilities.

01

Crypto agility management

Crypto agility introduces a new, difficult responsibility for hardware vendors to maintain and update cryptographic capabilities. Our platform helps device makers know when cryptography should change, what should replace it, and ways to update deployed products safely.

02

Secure hardware interfaces & PKI

The interface and chain of trust that links secure hardware on a device to IT software is a sensitive target. Our platform is engineered to make it easy, safe, and reliable to interact with QCIM products.

03

Device measurement and policy engineering

A Root-of-Trust should provide more than secure boot. We help device makers let IT and security teams know when a device continues to operate in a state its manufacturer and owner consider trustworthy.

Maintain control of device security after deployment.

Hardware vendors remain responsible for the security state and permitted behaviour of their products long after they ship. As disruptive technologies like quantum computing and AI change the operating environment, vendors need to adopt new capabilities while retaining that authority over deployed devices.

QCIM Platform Security equips hardware vendors with designs, tools, and research to ensure their products are secure-by-design within new 2030's era ecosystems.

Where it fits

Addressing what comes next.

01

Staying flexible to new threats and changes to cryptography

Quantum computing, AI-backed cryptanalysis, vulnerable implementations, and changing standards will force devices to adopt new cryptography after deployment, faster than ever before. BTQ connects continuing threat monitoring to tested software releases, secure update controls, and crypto-agile hardware so device makers can respond while products remain in the field.

02

Expecting more out of trusted silicon

Secure hardware will need to stay flexible with new customer expectations in management software, policy systems, and operational integrations. QCIM Platform Security connects trusted hardware to measurement, attestation, updates, recovery, and continuing cryptographic maintenance, turning a static component into an active platform for device defense.

03

Preparing for autonomous cyberdefense

AI agents will begin to play an active role in device security as the ecosystem evolves. Our approach helps autonomous cyberdefensive systems get the authoritative device evidence they need to stay ahead of the most persistent threats during runtime. AI may analyze evidence and propose actions, but the Root of Trust remains the deterministic authority.

Talk to us about platform security.

Request technical specifications, evaluation IP, or a consultation with our hardware security team.

Request evaluation →